Understanding MCP: The Model Context Protocol for Secure, Extensible AI Systems
Modern language models are extraordinarily capable — but historically, they have been limited to the information contained in their training data and whatever context a user provides at inference time.
By Ivan Pérez, at Parser
Modern language models are extraordinarily capable — but historically, they have been limited to the information contained in their training data and whatever context a user provides at inference time. The Model Context Protocol (MCP) addresses this limitation by defining a standardized, secure, and auditable way for AI systems to interact with external tools, services, and data sources.
MCP acts as the connector between large language models (LLMs) and the operational environments in which they are deployed. It empowers AI-driven applications to operate beyond basic text output, enabling controlled access to databases, filesystems, enterprise process pipelines, and a wide range of specialized computational services.
A useful analogy: MCP is the USB-C port for AI agents.
Just as USB-C standardizes how physical devices connect and exchange data, MCP standardizes how AI applications “plug into” external tools, services, and contexts. This gives organizations a modular way to augment AI capabilities, enforce strict governance, and avoid brittle, one-off integrations.
Why MCP Matters: Capability, Security, and Governance
MCP introduces a structured approach for exposing tools to LLMs, enabling:
- Access to external data sources (local or remote files, vector stores, operational databases)
- Execution of business workflows (pipelines, orchestrators, retrieval systems)
- Integration with enterprise tools (search APIs, internal services, calculators, domain-specific utilities)
- Dynamic discovery of new capabilities without redeploying or retraining models
Crucially, MCP does this without sacrificing security. Historically, LLMs lacked robust governance controls. MCP changes that by enforcing modern infrastructure principles:
- Least privilege: tools expose only what the model absolutely needs
- Strong isolation: each tool runs in a controlled sandbox or container
- Explicit permissioning: nothing is accessible by default
- Schema-based validation: all inputs/outputs follow strict, enforceable schemas
- Full auditable action logs: who accessed what, when, and through which MCP tool
For enterprises, this auditability and fine-grained access control are not optional, they are required to operationalize AI safely.
How MCP Works: A Discovery-Driven Client–Server Architecture
At its core, MCP follows a client–server architecture.
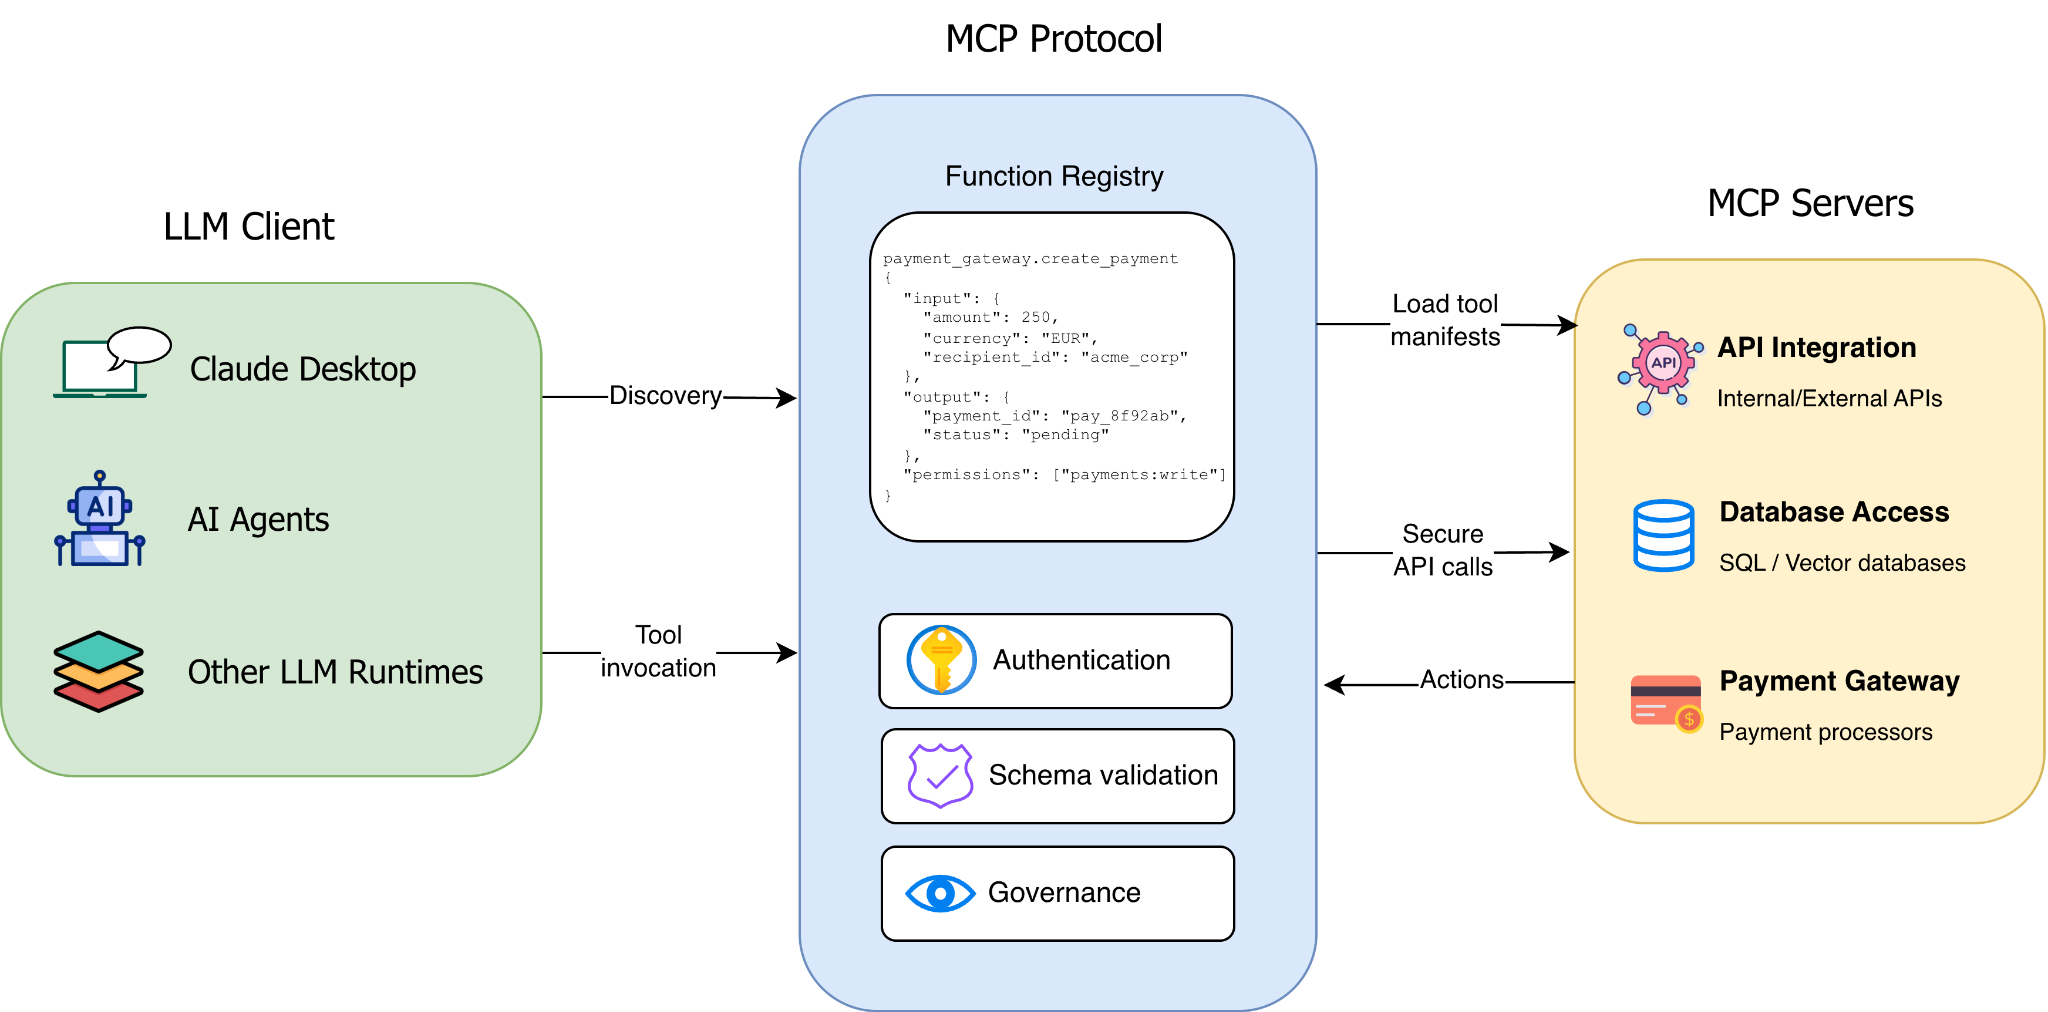
An MCP client, typically an LLM runtime or agent environment, connects to one or more MCP servers. Each server exposes tools, schemas, and capabilities that the client can safely invoke. The client never receives arbitrary code; instead, it interacts through well-defined, schema-validated operations, often acting as a mediator to external systems such as REST APIs, databases, or enterprise services.
This architecture enables LLMs to operate in a controlled environment where capabilities are discoverable, permissions are explicit, and integration points are standardized.
1. MCP Discovery Is Pull-Based, Not Push-Based
MCP clients do not passively wait for servers to announce themselves.
Instead, the client actively pulls information about available servers and their capabilities.
A typical discovery flow:
- The client is configured with a registry, directory, or explicit list of MCP server endpoints.
- On startup or on a fixed schedule, the client polls these endpoints.
- Each server responds with metadata describing its tools, input/output schemas, permissions, and operational constraints.
This process works much like a smartphone checking its app store for updates:
the client requests information, rather than servers pushing unsolicited capabilities.
This approach ensures tight security boundaries and avoids accidental exposure of tools or data.
2. Optional Server Registration via Discovery Services
In more advanced or enterprise environments, MCP deployments often introduce a discovery service to manage large numbers of servers.
A typical pattern looks like this:
- A central MCP Registry maintains authoritative knowledge of available MCP servers.
- MCP servers auto-register themselves when they come online.
- Clients periodically query the registry to retrieve an updated list of server endpoints.
Functionally, this acts like a DNS layer for MCP tooling enabling dynamic, centrally managed discovery.
This is especially useful for:
- Organizations with multiple departments exposing different MCP tools
- Multi-region and multi-cluster infrastructures
- Automated onboarding/offboarding of tool capabilities
- Highly modular internal environments where tools evolve frequently
Clients no longer need hard-coded configurations; discovery becomes dynamic and policy-driven.
3. How the Client Learns About New Capabilities
Once a client connects to a server, either directly or through a registry lookup, the server responds with a tool manifest.
This manifest contains all the structured information the client requires to safely interact with that server.
A manifest typically includes:
- Tool names and endpoints
- Input/output schemas (commonly JSON Schema)
- Permissions and scopes
- Configuration parameters
- Operational policies and safety metadata
Clients usually cache the manifest and refresh it periodically.
Because the protocol is schema-driven:
- New tools can be added without updating the client’s code.
- Capabilities become hot-swappable, since the client interprets the manifest dynamically.
- LLMs remain safely within defined operational boundaries.
This is one of MCP’s core advantages: extensibility without loss of control.